Since our last product update, our development team hasn’t sat still. Here is what is new in Modat Magnify.
479 New Fingerprint Rules
Magnify recognises many more products, such as Apache Doris, Apache SkyWalking, Alibaba Nacos, Amazon DCV and Airbyte, plus many IoT, industrial, energy and router products. New fingerprints are also available for tracking malicious infrastructure. Searching by product is on the Enterprise plan.
New Protocols
Magnify now detects 20 more protocols that answer over UDP, such as SSDP, NetBIOS, CoAP and IPMI. Try protocol=ssdp.
FRP is new too: find FRP servers with protocol=frp. It is a popular tool to make internal services reachable from the internet, and attackers often use it to keep access to networks they broke into.
You can also find L2TP VPN servers with protocol=l2tp. Magnify now scans UDP port 1701 and already lists millions of L2TP services.
IPMI, WDBRPC, pcAnywhere and L2TP are on the Enterprise plan; the other protocols are on all plans.
Find Anything by Its Hash
Paste an MD5, SHA-1 or SHA-256 hash into free text search, without a field name, and Magnify finds the services where that hash appears, such as a banner, page body or certificate hash.
See Which Servers Support Multipath TCP
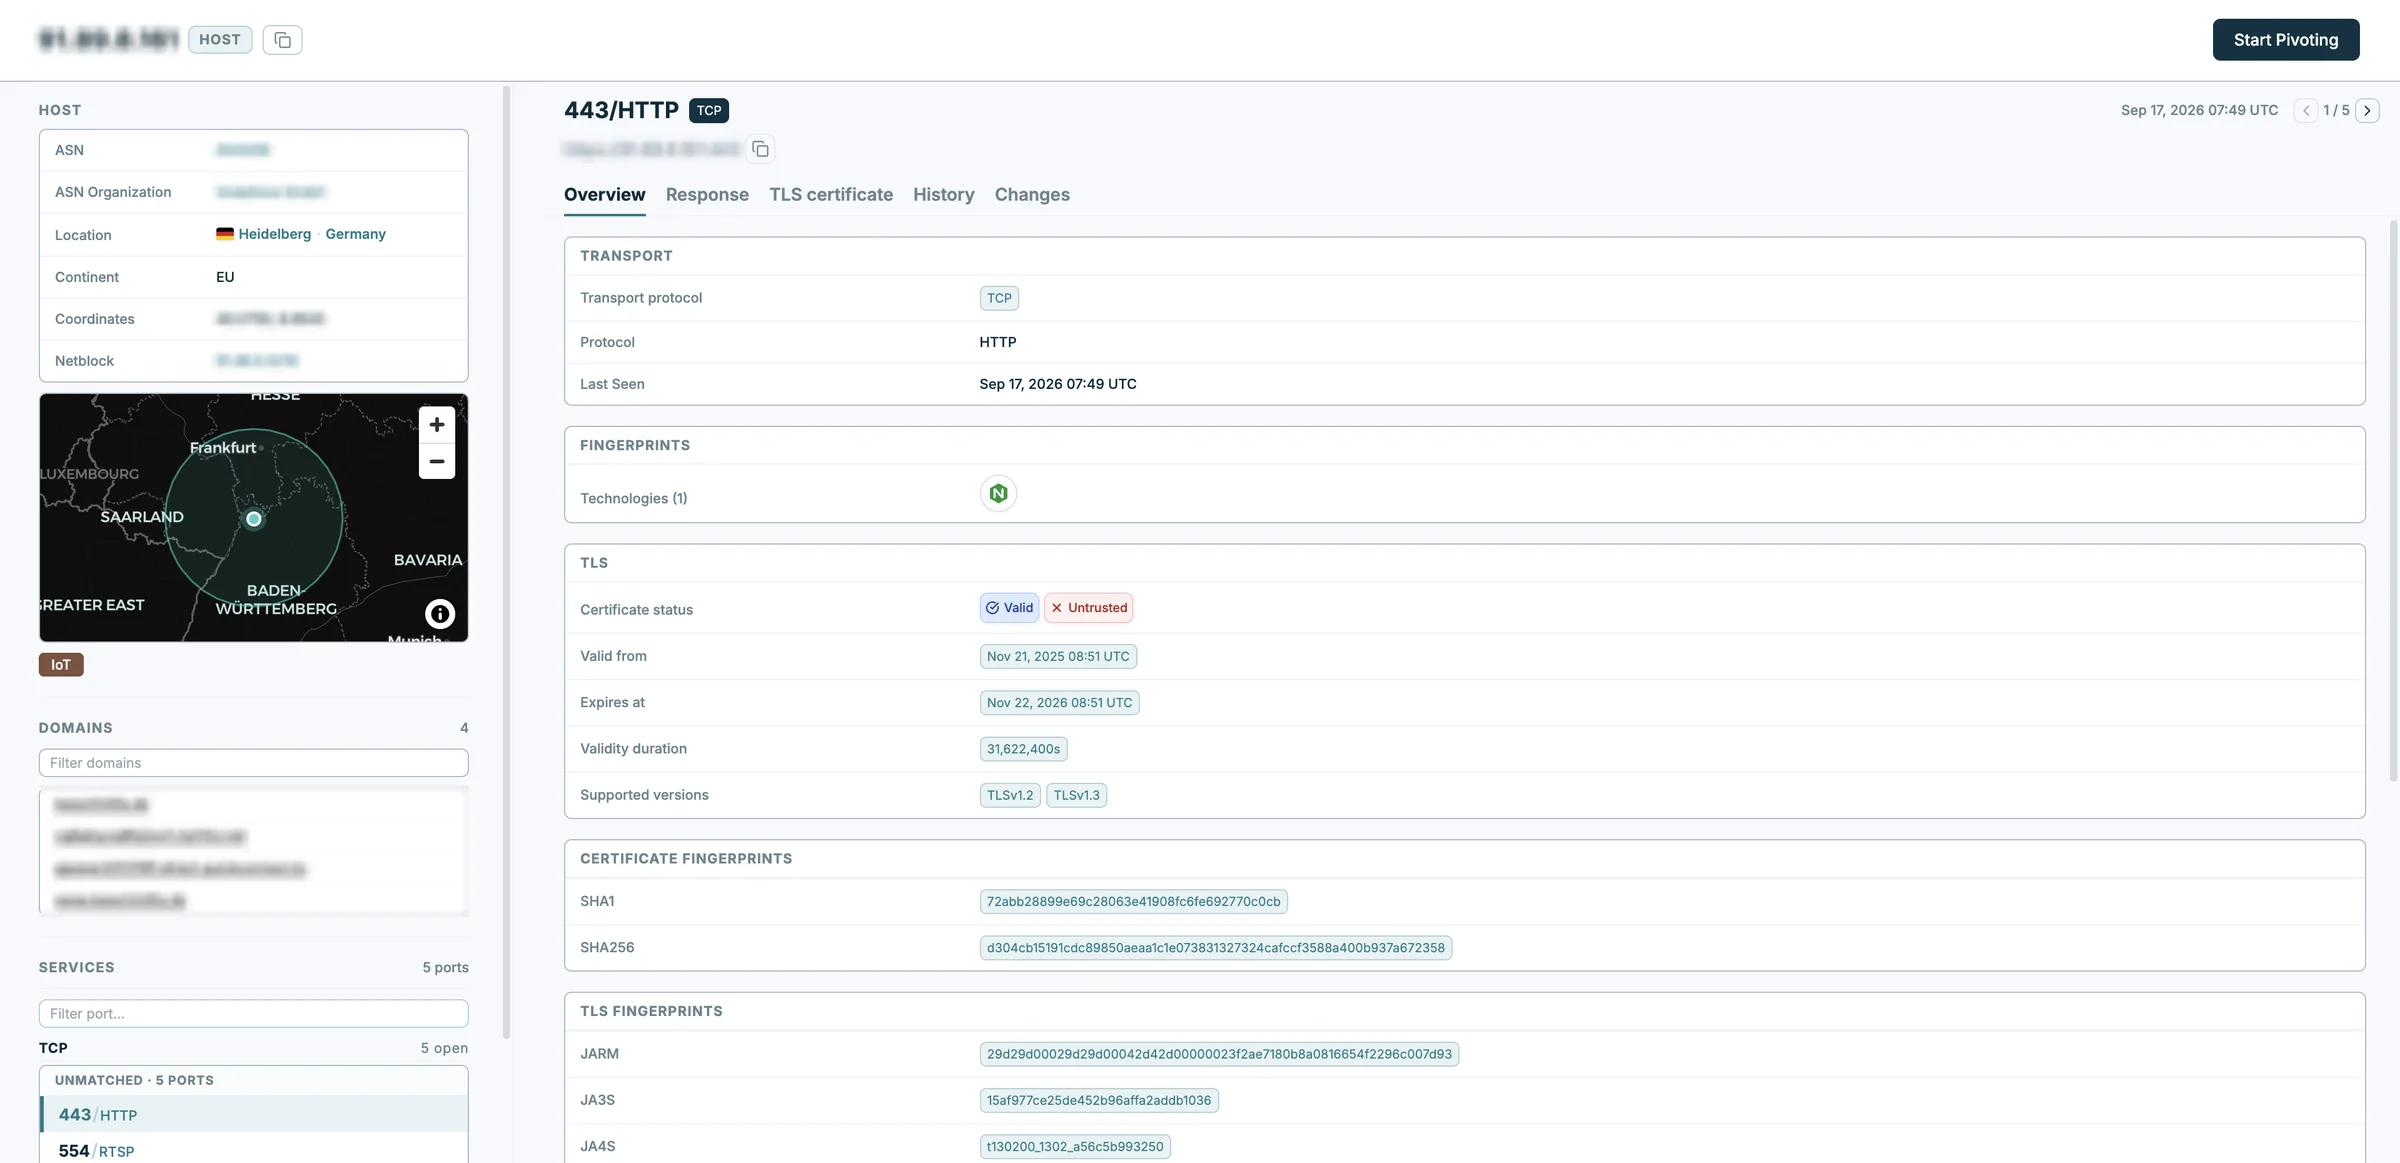
Search results now show whether a service supports Multipath TCP, and you can search for it with tcp.mptcp=true.
Search by Continent
Host and service search have a new continent filter that takes a name or a code, for example geo.continent_code=Europe or geo.continent_code=NA. Domain search (Enterprise) can also filter on the continent where a domain’s IP is located.
See CVEs on Service Results
Service search results now show the possible CVEs for each service, the same way host results already did.
The Query Language Spec Is in the API
API users can fetch the full query language spec from the Magnify API: every searchable field, its type and the operators it accepts. That makes it easier to build integrations and AI tools on top of Magnify.
Copy Any Docs Page as Markdown
Every docs page has a Copy as Markdown button. Paste the page straight into an AI assistant or your own notes, with the headings, tables and examples intact.
More Pivot Points in Threat Investigator (Enterprise)
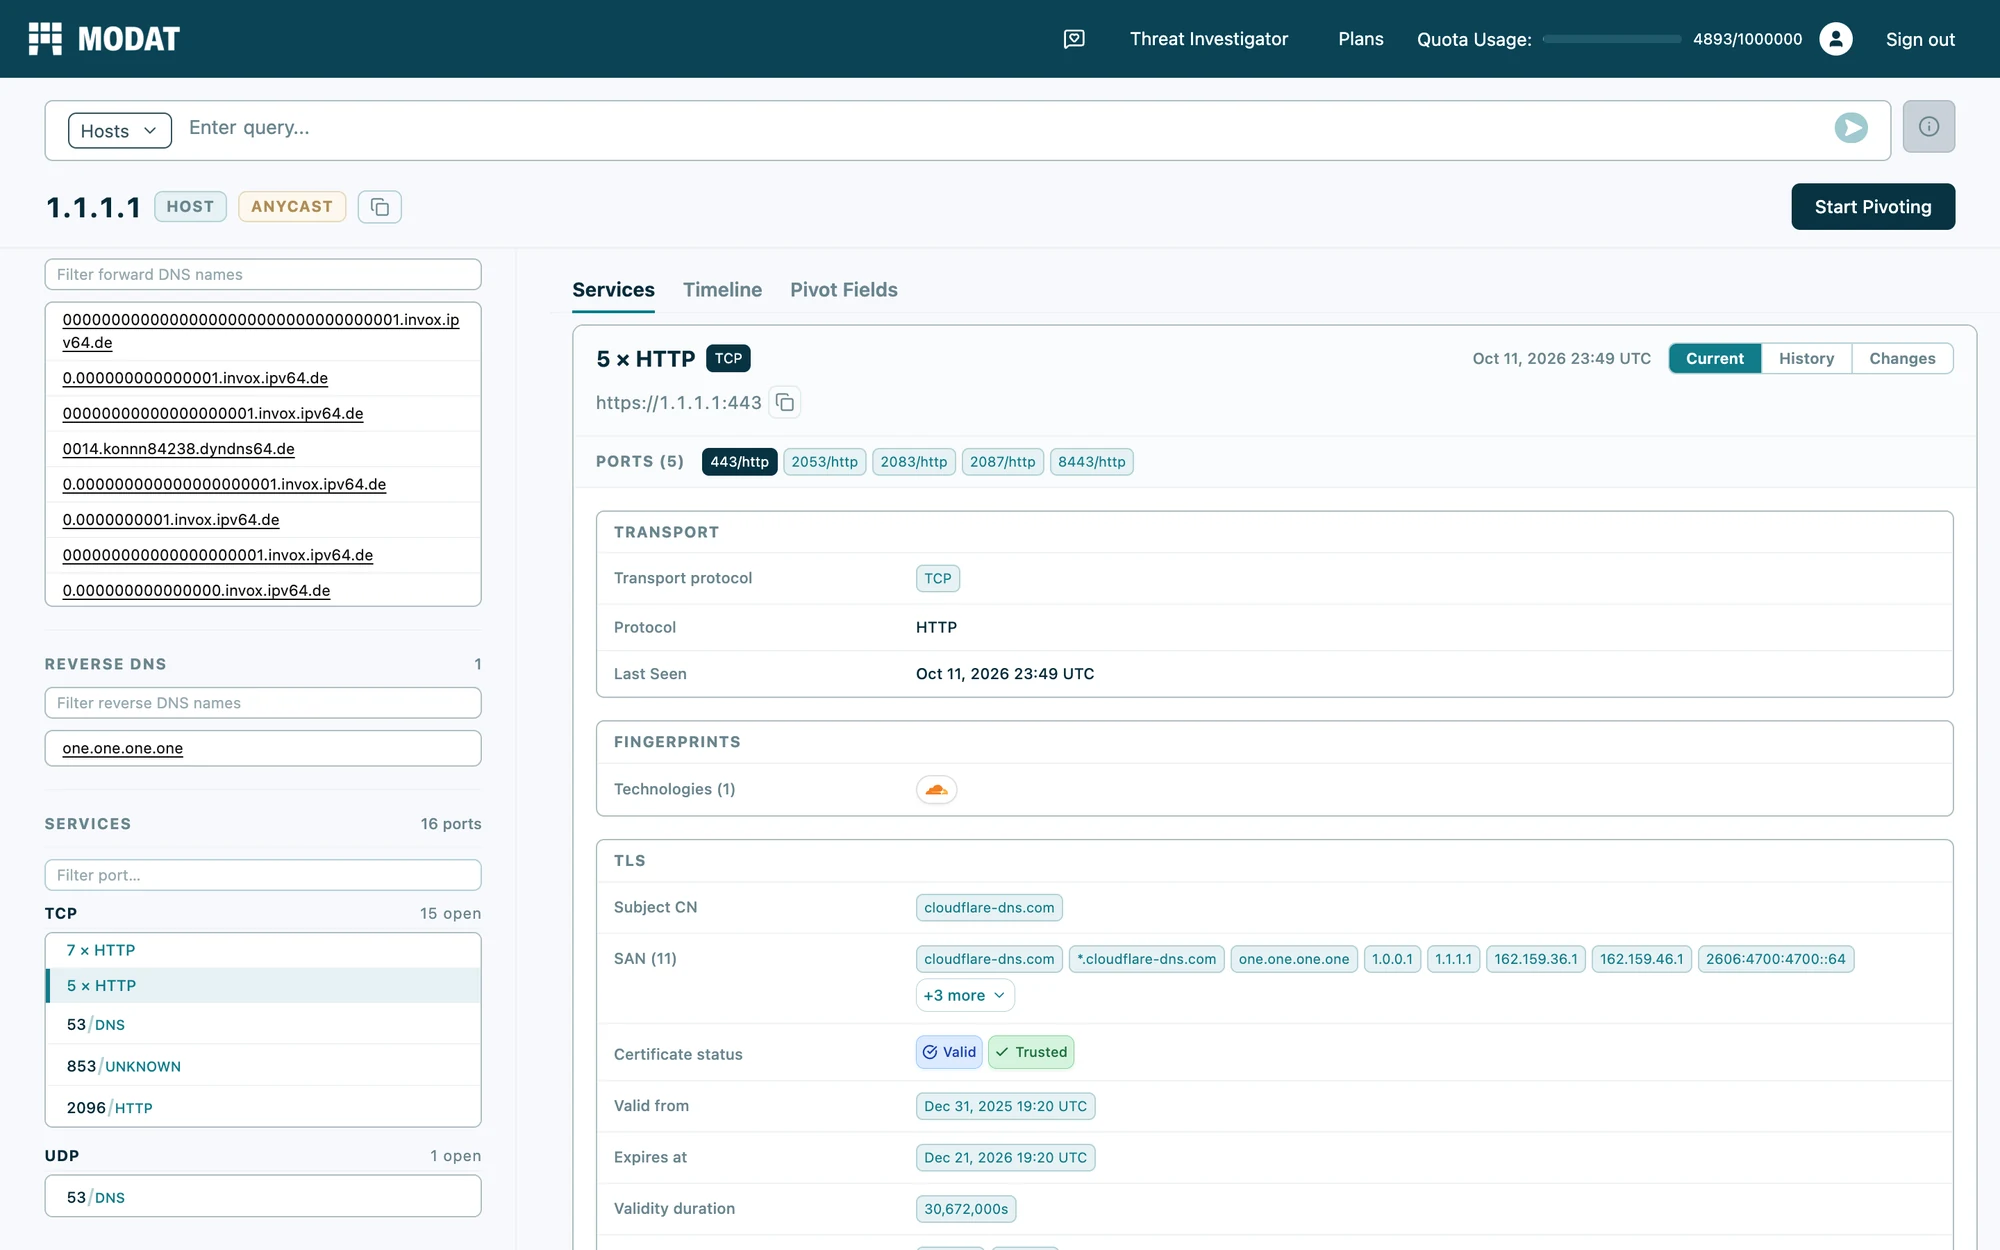
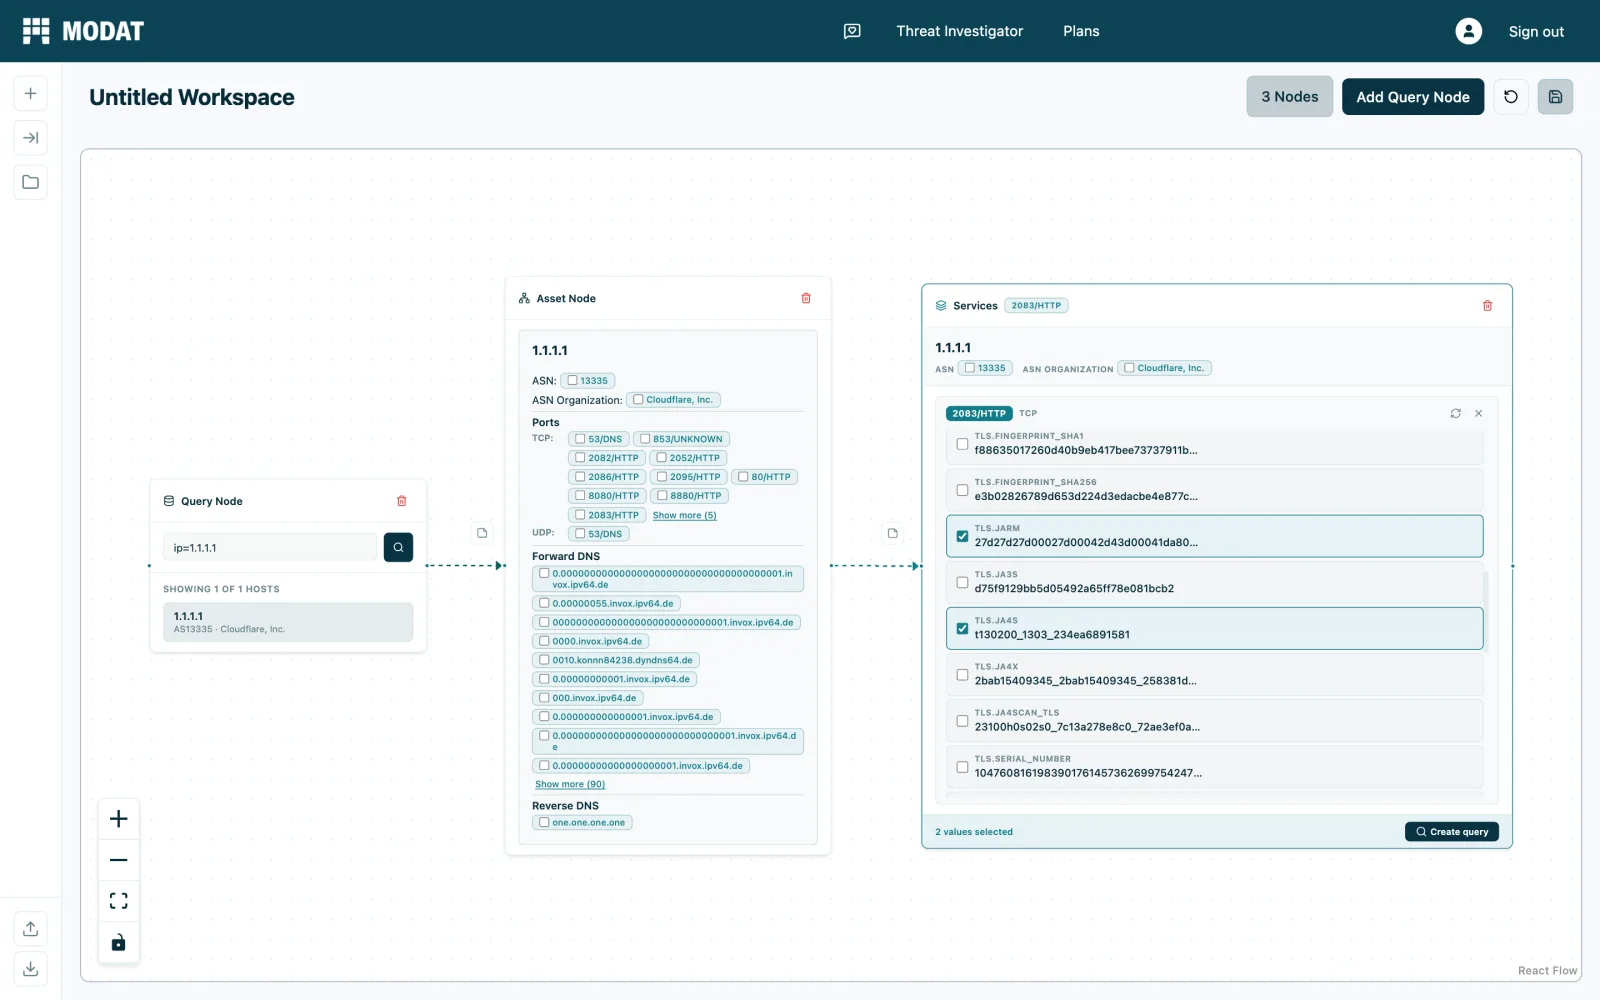
Threat Investigator now offers every TLS fingerprint as a pivot: JARM, the certificate SHA-1, and JA3S, JA4S, JA4X and JA4Scan-TLS. Tick the values you want, create a query, and jump from one server to others that share its TLS setup.
Search DMARC Records in Passive DNS (Enterprise)
Passive DNS now collects DMARC records, which set a domain’s email policy. Find domains with one using rrtype=dmarc, or search the policy itself, for example records.dmarc.value~p=reject.
See Ports That Are No Longer Seen in the Search Results (Professional and Enterprise)
The detail card in the search results now also lists the ports a host had within your plan’s history period that are no longer seen. Click one to see its last scan and go through its history.
All features are live on the platform now. Explore them at magnify.modat.io, read how to use them in the documentation, or reach out to the team at support@modat.io with any questions.