Security Operations
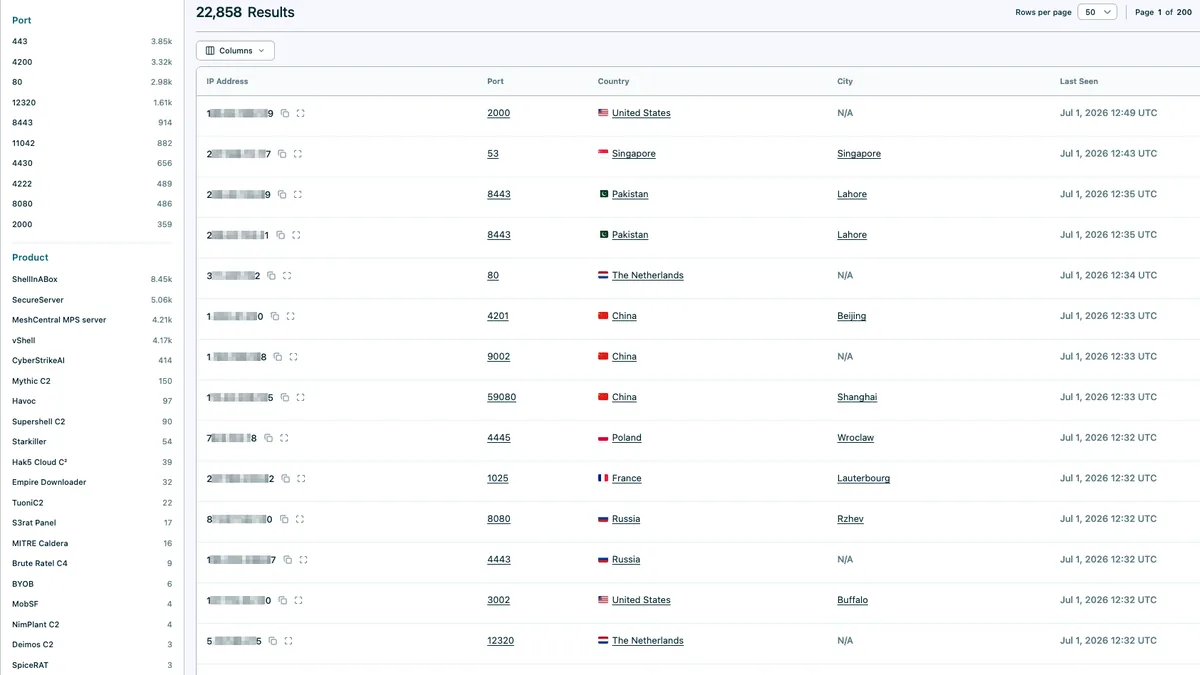
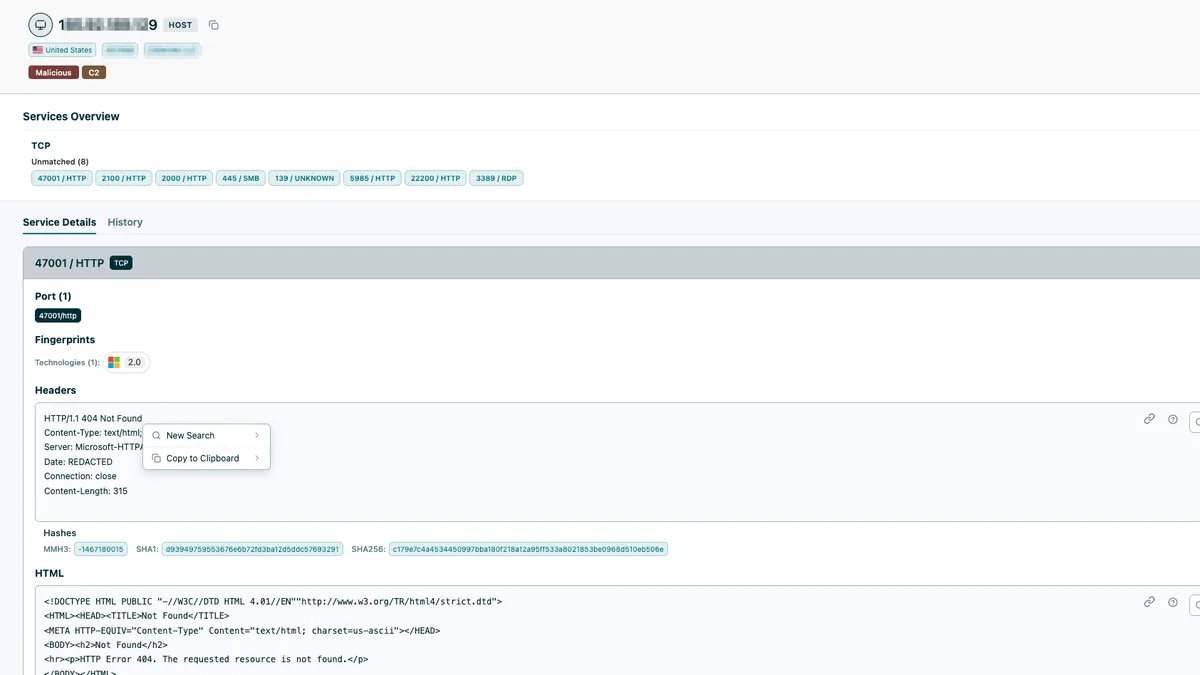
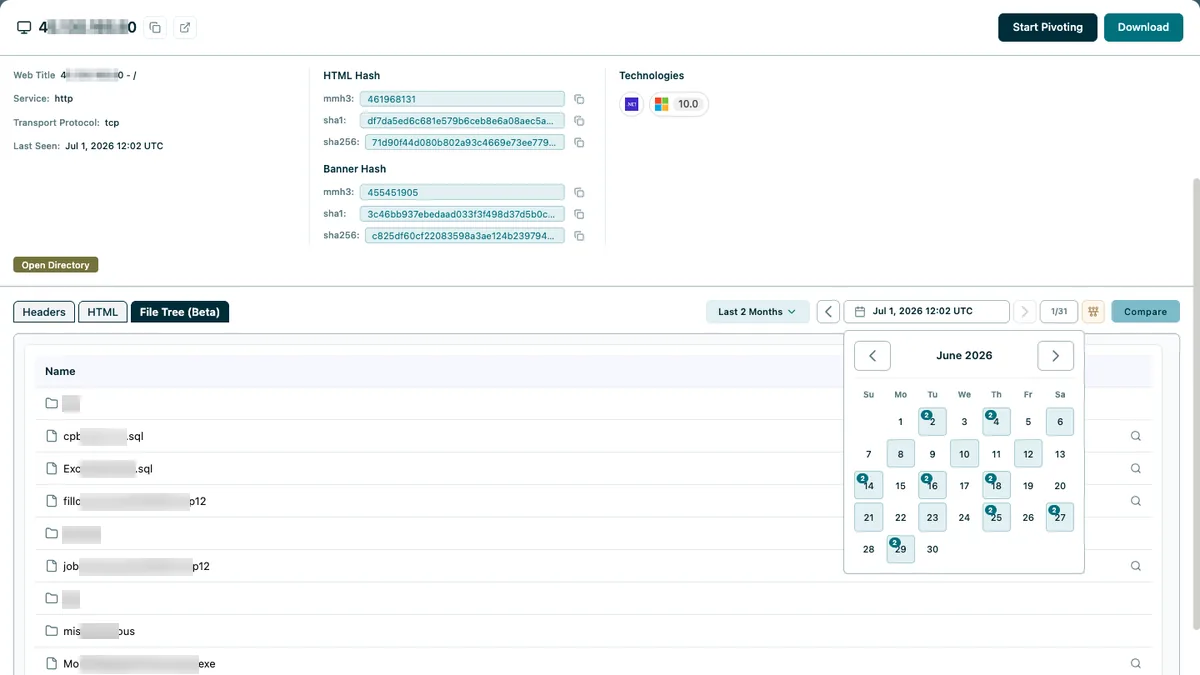
Instead of manually enriching each alert by jumping between the SIEM, threat feeds and ad hoc lookups, analysts get infrastructure context attached the moment an alert appears.
Related infrastructure is already mapped. Historical behaviour is already available. Triage starts with context instead of collecting it. Over MCP, an agent enriches the alert before anyone opens it.
SOC teams are expected to triage and respond to incidents faster than attackers can exploit them. In reality, analysts spend most of their time manually enriching alerts, pulling context from multiple disconnected tools before they can even determine whether an alert is real.
Threat feeds generate noise as often as signal. Without infrastructure context attached to the alert itself, every investigation starts from zero, and incidents are handled as one-off events rather than part of a continuously monitored picture.
our capabilities
Four capabilities, one workspace.